Audit readiness

Readiness,
walked.

Varða takes your team control by control through the framework, tests what you can actually show, and turns every gap into an owned task.

Click a stone, or a mark on the screen, to see how each part connects.

Five stones, one route.
CONTROL SELECTION · LIVE SCREEN
Frameworks supported ISO 27001APRA CPS 234APRA CPS 230NIST CSFACSC Essential 8SMB1001SOC 2ISO 22301

Two ways in

Start deep, or start in five minutes

Same engine either way. One is a full evidence-first assessment; the other tells you whether a single policy holds up.

Framework assessment

Control-by-control, evidence first

Work the whole control set with your team. Attach the evidence you actually have, test it, and see exactly where the file is thin, then hand a board-ready report to the people who need to sign it off.

Every control mapped, scoped and owned
Evidence requests tracked to close-out
Control testing with a written conclusion
Board-ready PDF reporting
Request a walkthrough

Quick policy test · free

One document, one answer

Drop in a single policy. Varða reads it against the framework you pick and tells you what a reviewer would question. No login needed to try it.

Access control · Incident response · BCP …
Any policy document you already have
Run a free test →

The trail

What the tool actually looks like
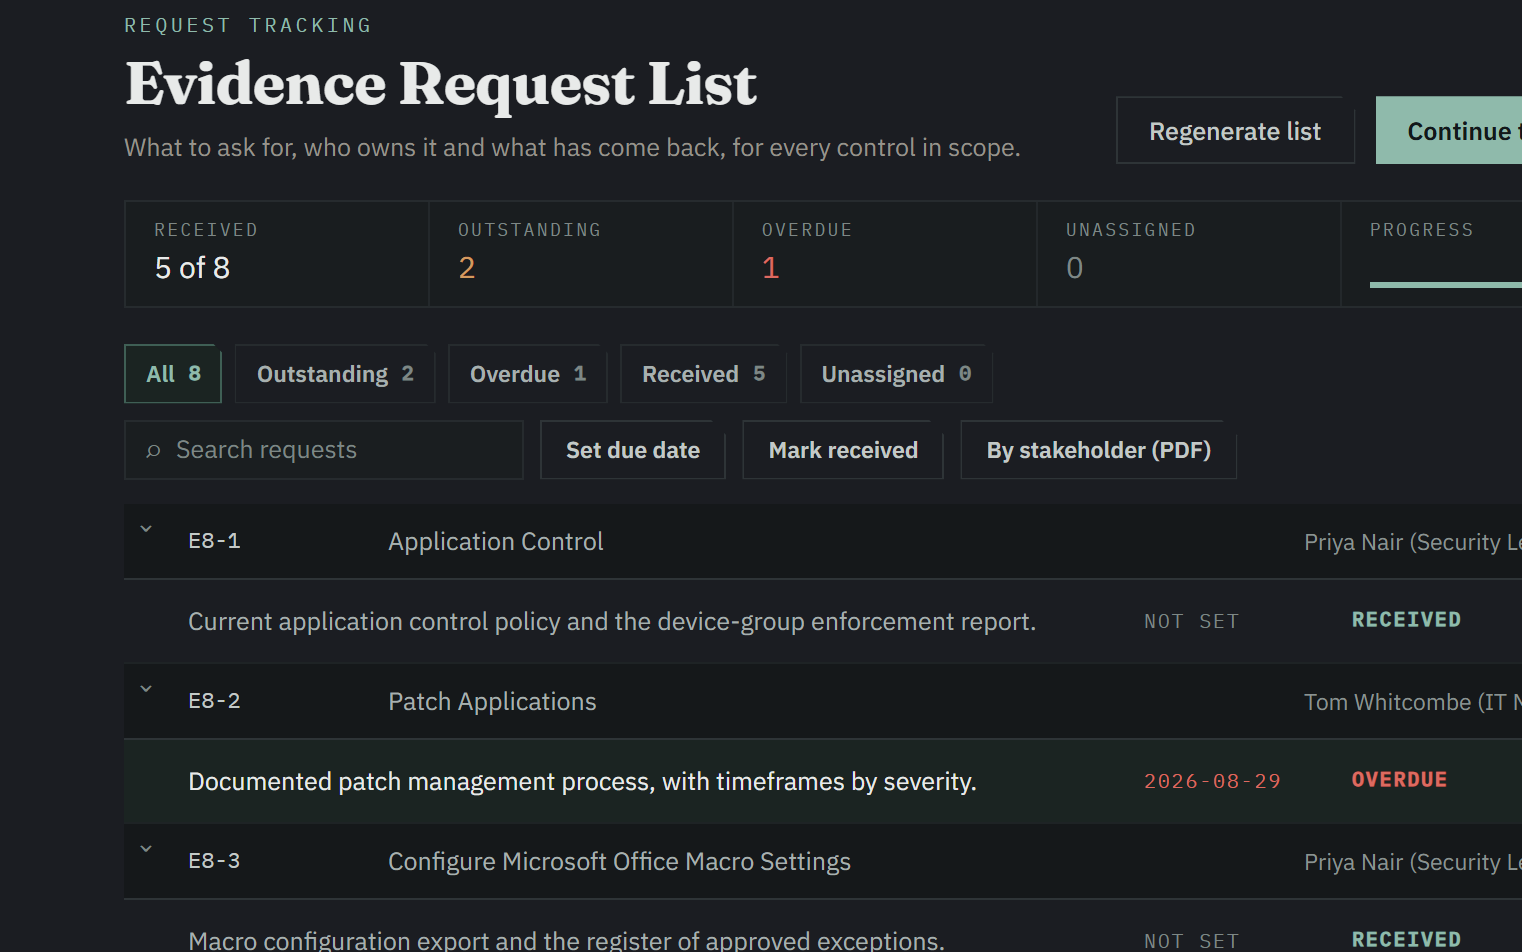
Evidence Request List for Essential 8 showing the review workspace navigation and a received/outstanding/overdue evidence-tracking donut chart
01

Evidence Request List

Every control's evidence tracked in one place, from stakeholder to status to upload.

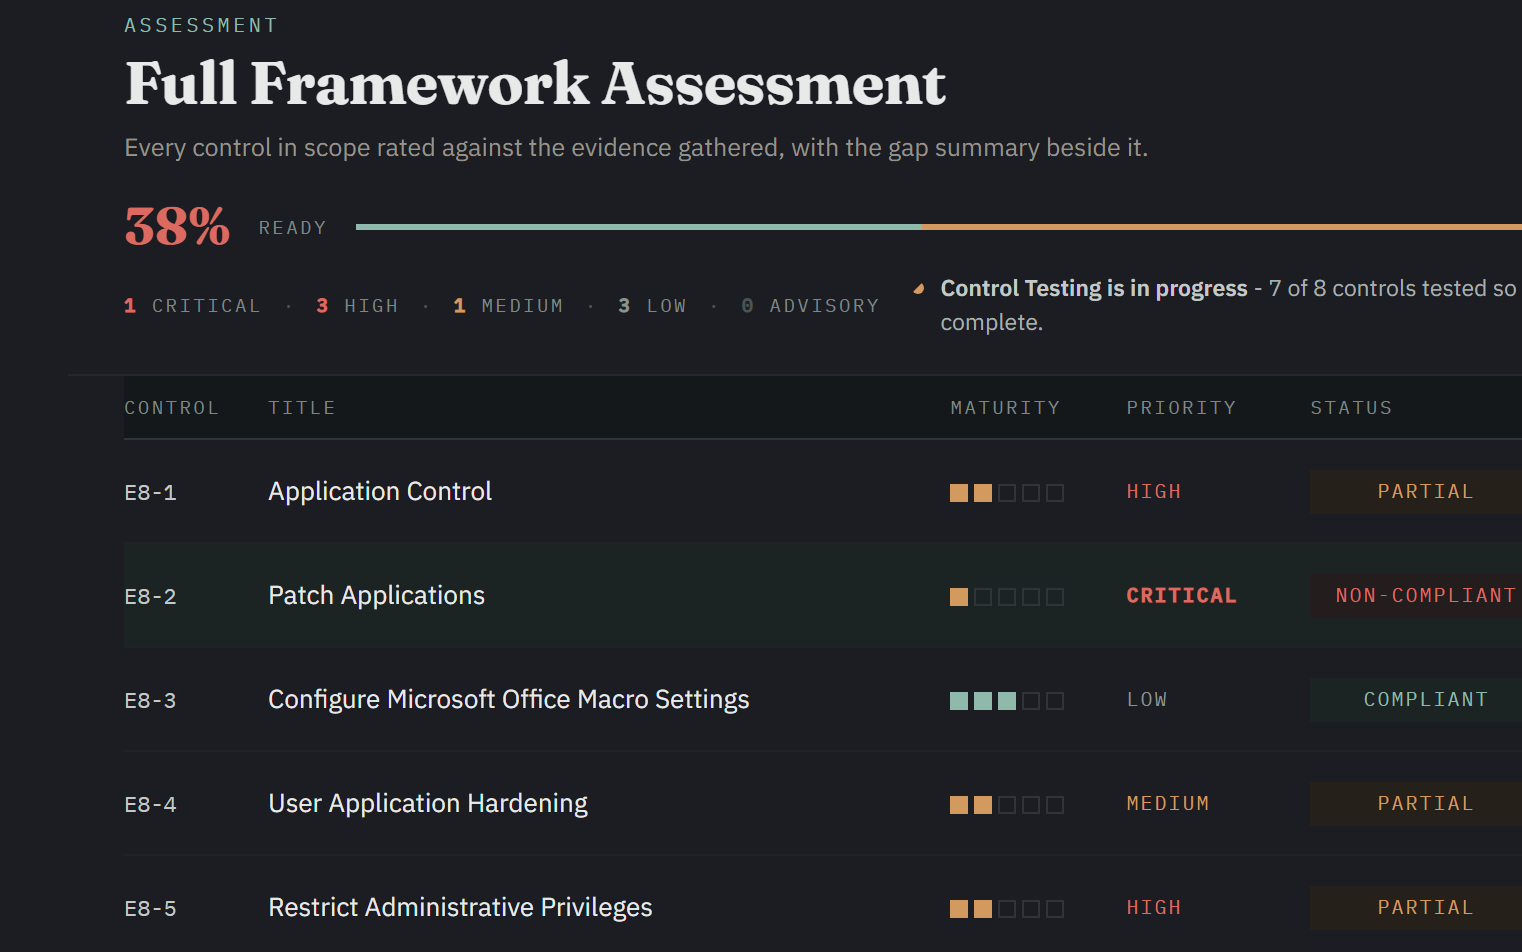
Full Framework Assessment results screen showing the Overall Readiness compliance summary and the start of the per-control results table
02

Full Framework Assessment

Live compliance and priority breakdowns as every selected control is assessed.

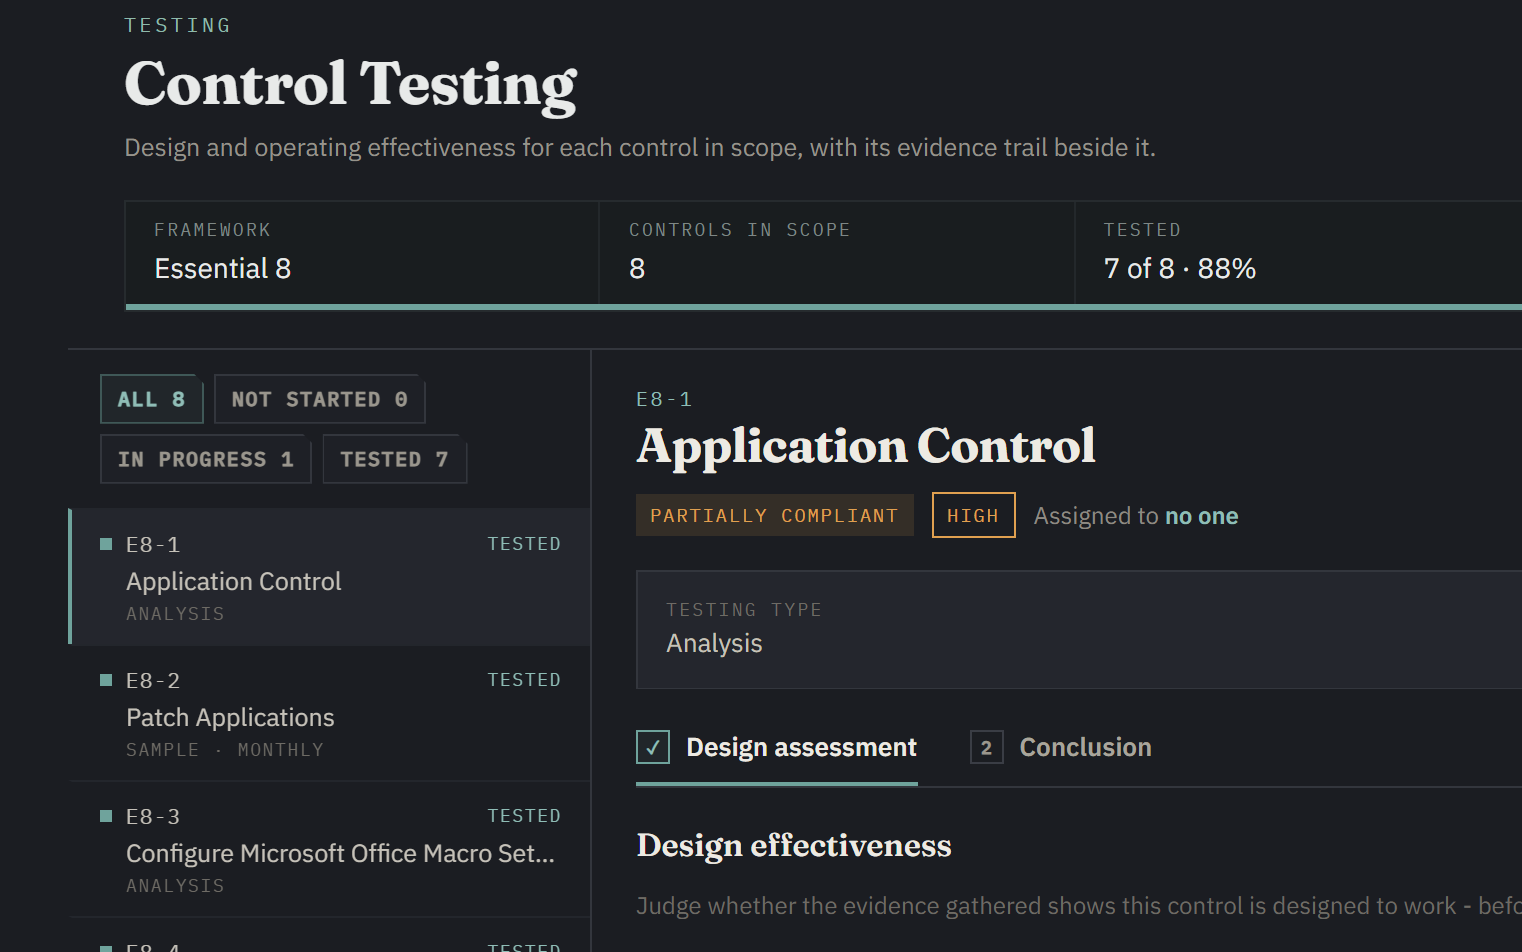
Control Testing dashboard showing testing progress, the Analysis/Sample testing-approach breakdown, and a sidebar list of tested controls with status and testing-type badges
03

Control Testing

Sample and analysis-based effectiveness testing per control, backed by real evidence.

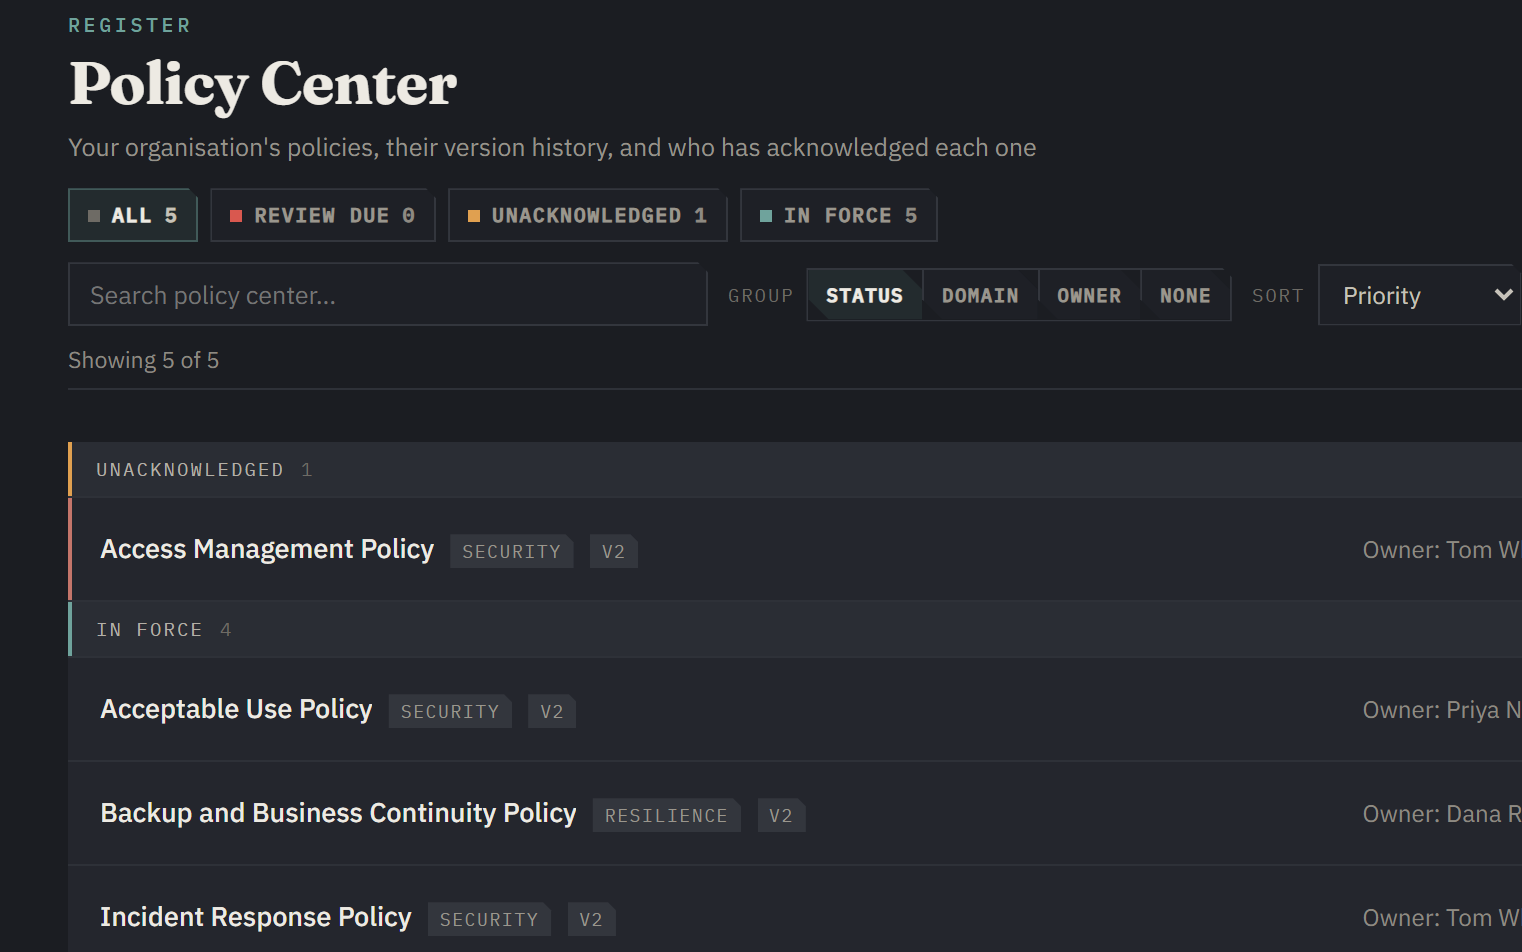
Policy Center showing policy documents with version history, real staff acknowledgements, and controls each policy is tagged to
04

Policy Center

Version history and real staff acknowledgements, tagged to the controls they cover.

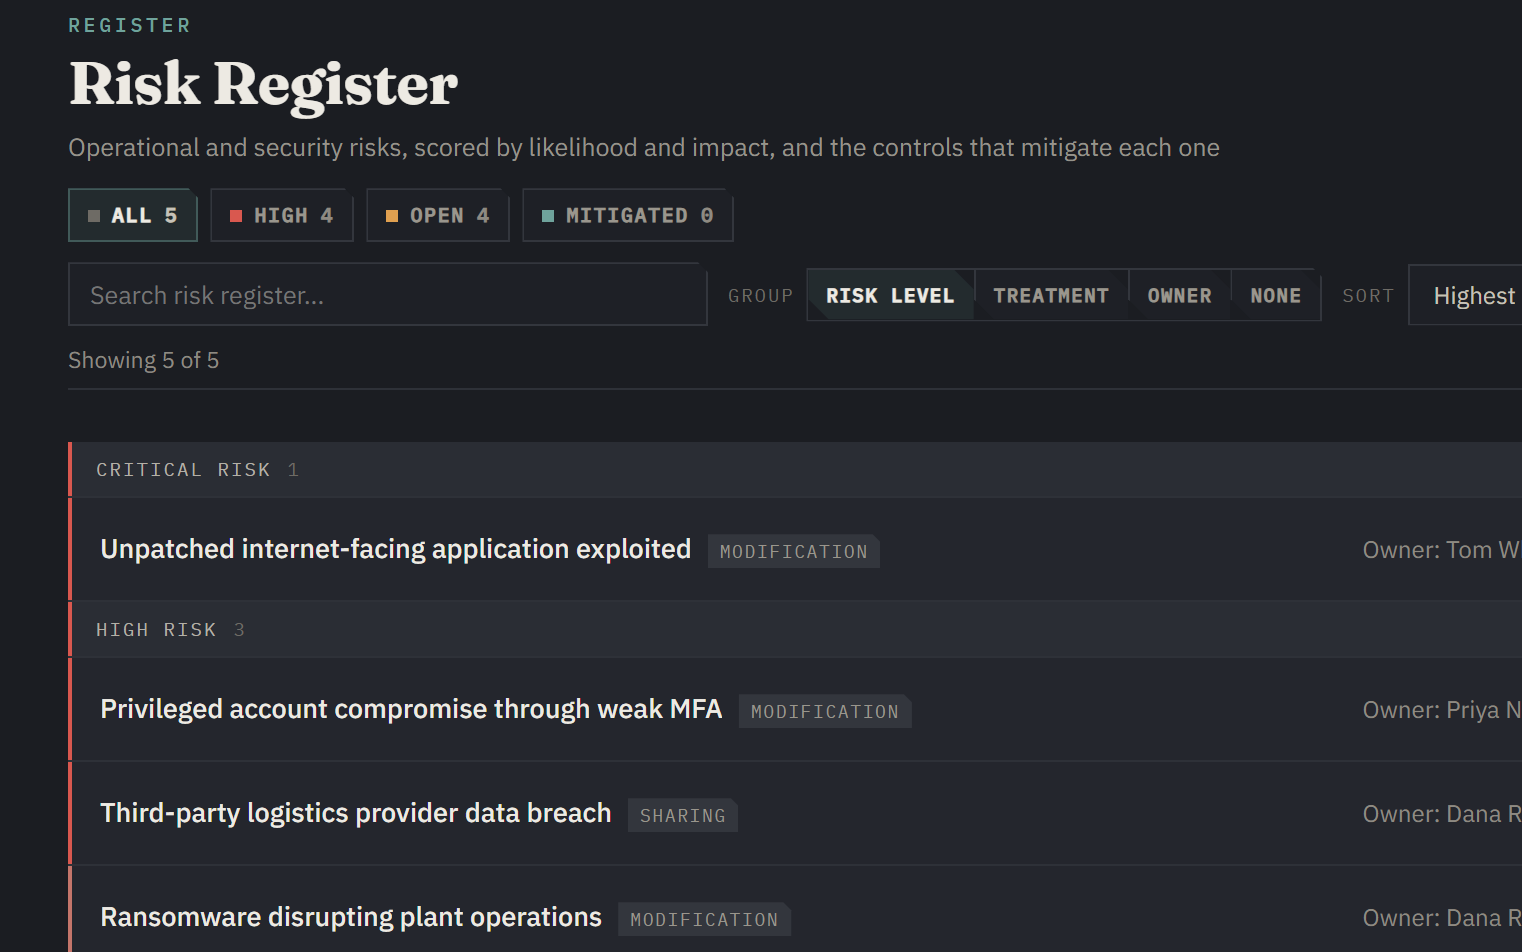
Risk Register showing operational and security risks scored by likelihood and impact, with owners, treatment plans and linked controls
05

Risk Register

Risks scored by likelihood and impact, linked to the controls that mitigate them.

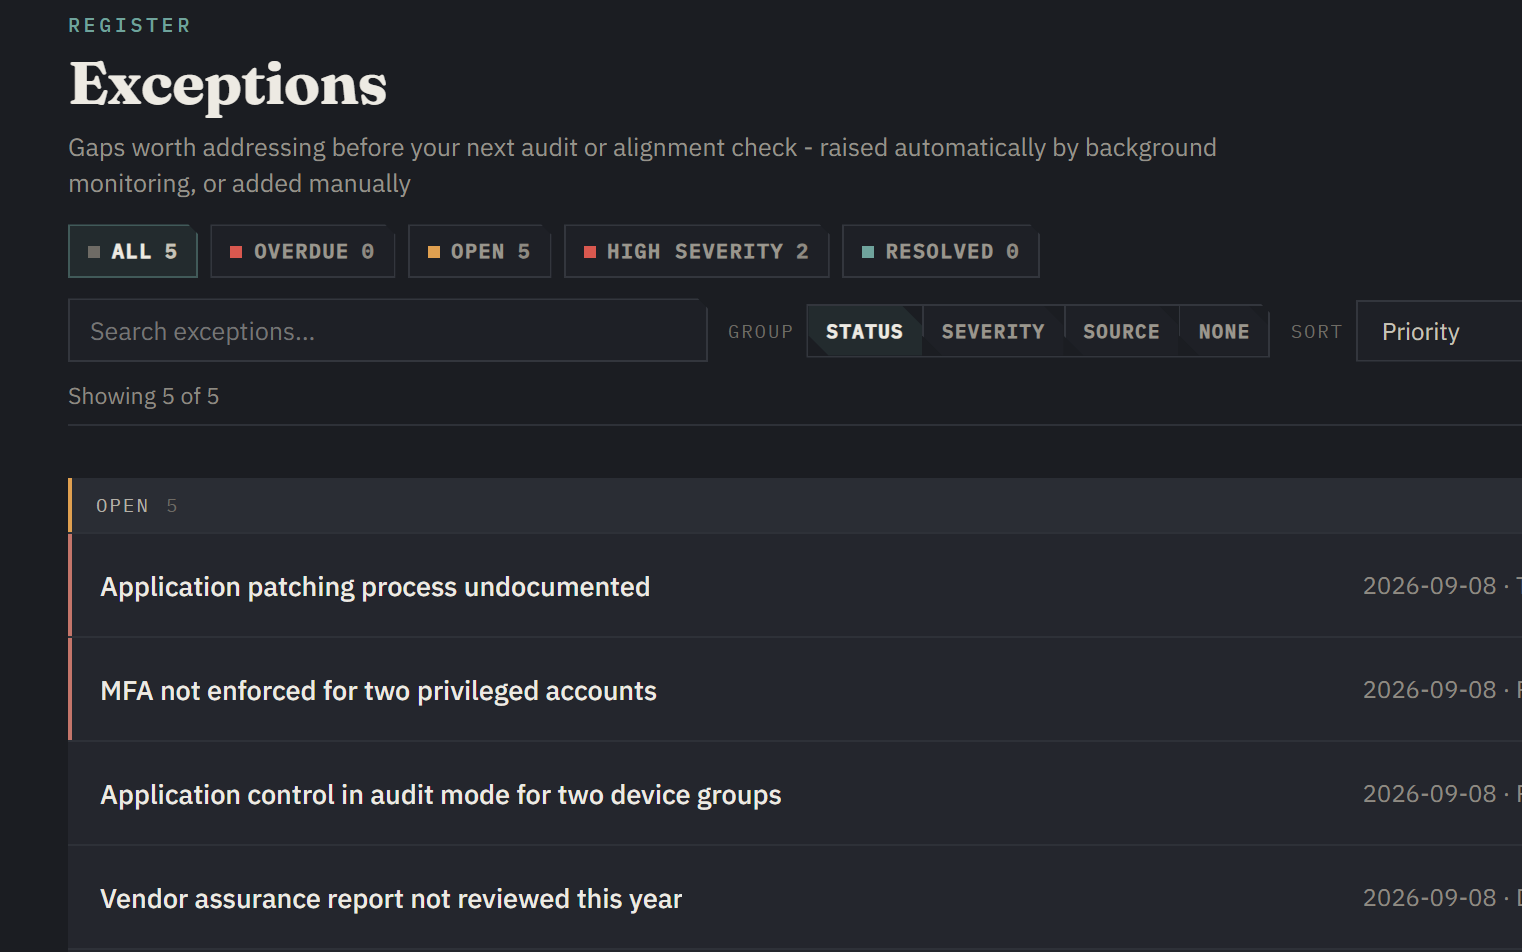
Exceptions register showing gaps flagged automatically or raised manually, with severity, status, due date and recommended action
06

Exceptions

Gaps flagged automatically or raised manually, tracked with an owner and a due date.

How it works

Four stones, in order

Each step sits on the one below it. Skip a stone and the stack won't hold, which is exactly how audits fail.

Stone one

Set the scope

Pick the framework and tell Varða what's in scope: entities, systems, the bits you outsource. It loads the control set and drops the questions that don't apply to you.

Stone two

Work the controls

One control at a time, in plain language. Answer, attach what you have, assign what you don't. Varða marks the difference between a claim and evidence for it.

Stone three

Test and close the gaps

Test the controls that matter, record what you found, and chase the open evidence requests until the list is empty. This is the work an auditor would otherwise find for you.

Stone four

Report before the audit

Export the readiness picture as a PDF your board or your auditor can read cold: gaps, owners, remediation order. Then walk into fieldwork knowing what they'll find.

In practice

What this looks like on a Tuesday

09:40

"Which access reviews are we missing?"

You open the control, see two quarters evidenced and one empty, and raise the request against the owner, before anyone asks you for it.

14:15

A policy that reads well but doesn't hold

The Quick Policy Test flags the clause a reviewer would push on: an obligation with no owner and no review cycle attached to it.

17:00

Something to send upstairs

Export the report. The risk committee gets the gap list and the remediation order in language they already use, no screenshots of a tool.

Comparison

Where Varða sits

Between a spreadsheet you maintain by hand and a full GRC platform you have to implement. Readiness, not continuous compliance theatre.

SpreadsheetGRC platformVarða
Set-up before you can startHours of tab-buildingWeeks of implementationPick a framework and go
Control-by-control questioningWhatever you wroteConfigurableWritten by an auditor
Evidence tracked to an ownerEmail threadsYesYes, with request states
Control testing and conclusionsNoneSometimesBuilt in
Board-ready reportingManual deckDashboard exportsPDF report, written for committees
Fits an SMB or a small audit teamYes, painfullyOver-scopedYes
Ōthala · what is yours to hold
Today
Varða, solo-built
Public sector
Queensland Audit Office
KPMG
Technology risk advisory
Deloitte
Audit and assurance

Who built it

Built by someone who has sat on both sides of the fieldwork table

Varða is solo-built by an audit and risk advisory practitioner with Big 4 background across Deloitte and KPMG, plus public-sector audit work at the Queensland Audit Office. Every control question in the product is written the way it would be asked in a real assessment, because it has been.

That also means you talk to the person who built it. No tiering, no handoff.

Request a walkthrough

See the path before you're standing on it

A short walkthrough, direct with the founder. Not a sales queue. Thirty minutes, your framework, your scope, we'll walk the assessment with your own controls in front of us.

Prefer to just try it? Run a free Quick Policy Test →

No commitment, just a real conversation, not an automated funnel.